Solutions

Six problems we help organisations fix.

Most organisations already own plenty of security tools. These solutions sit alongside what you have, start from intelligence, use AI to keep pace with attackers, and keep accountable people in charge of the decisions.

Intelligence-led defence

The problem

Security tools raise thousands of alerts with little context about this region, and the important ones get lost.

Involves

Threat intelligence, network detection and response, protective DNS, compromise detection.

What changes

Alerts are ranked using intelligence on the threats active in Southeast Asia, so your team looks at the most relevant ones first.
AI-assisted security operations

The problem

Analysts spend most of the day on repetitive triage and evidence gathering, while real threats wait in the queue.

Involves

Multi-agent AI SOC platform, generative AI assistant, threat intelligence, your existing SIEM and EDR.

What changes

AI agents do the triage and enrichment. Analysts spend their time on decisions, and every consequential action has an accountable person behind it.

Saibergard supplies security operations software and technology only. We do not provide managed security operations centre (SOC) monitoring services.

Securing AI adoption

The problem

Teams adopt AI assistants, agents and plug-ins faster than anyone can check them, and attackers have started to target AI directly.

Involves

AI security guardrails, AI agent supply-chain security, discovery of AI in use, governance policy.

What changes

AI in use is visible, its add-ons are vetted before approval, and guardrails keep prompts, tools and outputs within policy.

Continuous exposure validation

The problem

A yearly penetration test shows how things stood on one day. Your configuration changes every week.

Involves

External attack surface management, automated and AI-assisted penetration testing, control validation.

What changes

Regular automated and AI-assisted testing shows whether your controls still stop real attack techniques, with evidence to support audits.

Digital risk protection

The problem

Impersonation sites, fake apps and leaked credentials harm customers and trust before anyone inside notices.

Involves

Impersonation and brand protection, leaked data and dark-web exposure, takedown support.

What changes

Early warning of impersonation and leaks, with the evidence needed to have them taken down.

Expert testing and regulatory readiness

The problem

Automated tools find known issues. High-impact risks and regulatory reviews still call for skilled human testing.

Involves

Penetration testing, red teaming, architecture review, compliance mapping.

What changes

Manual testing and governance work lower real risk and produce evidence to support audit and regulatory reviews.

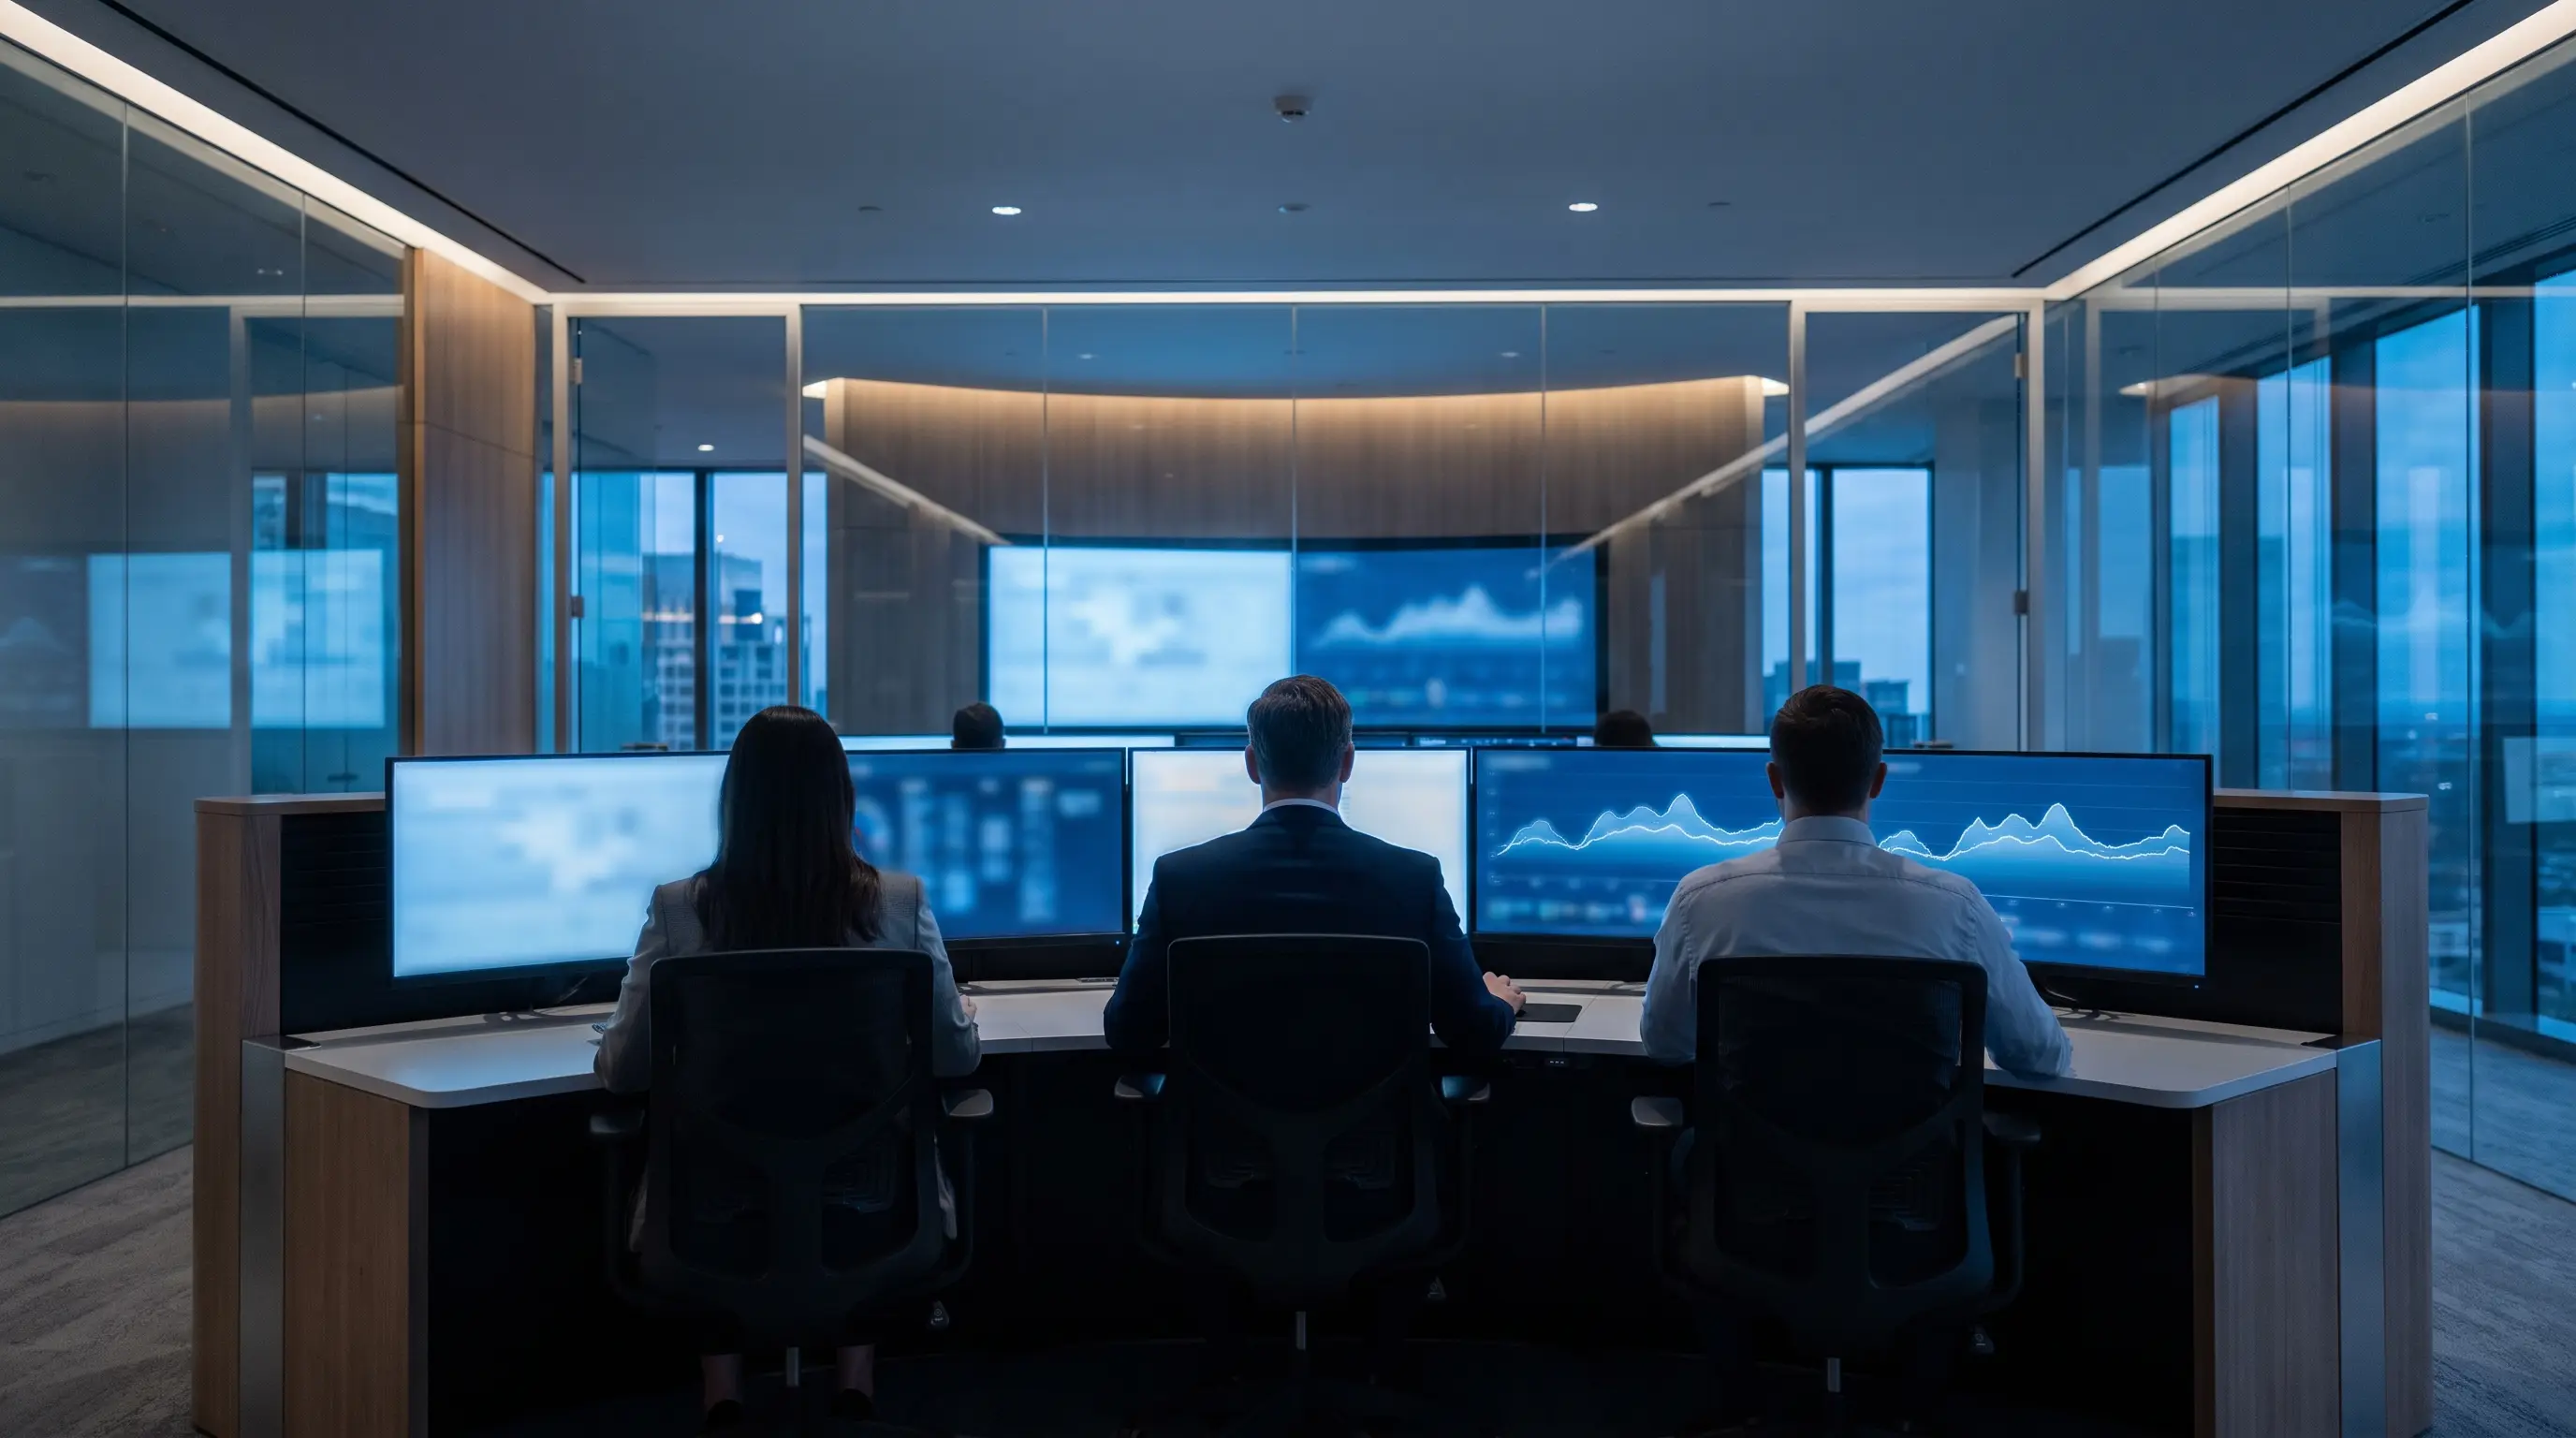
Security analysts reviewing alerts on several screens
Your team stays in charge: AI prepares the evidence, your analysts decide.
The cycle

How the pieces fit together

  1. 01

    Know

    Intelligence on the adversaries targeting you

  2. 02

    Find

    What they can reach, inside and out

  3. 03

    Prove

    What can actually be exploited

  4. 04

    Respond

    AI-assisted detection and containment

  5. 05

    Verify

    People confirm, fix and improve

Then back to step one, with what you learned

We don't quote headline percentages. Results depend on your environment, so we measure them against your own baseline during a scoped proof of value.

Ask about a proof of value.

We scope it around your environment and measure the results against your own baseline.